

Practice Test for 300-410 Certification Real 2026 Mock Exam
Prepare For Realistic 300-410 Dumps PDF - 100% Passing Guarantee
NEW QUESTION # 419
Refer to the exhibit. R1 is configured with uRPF, and ping to R1 is failing from a source present in
the R1 routing table via the GigatxtEthernet 0/0 interface. Which action resolves the issue?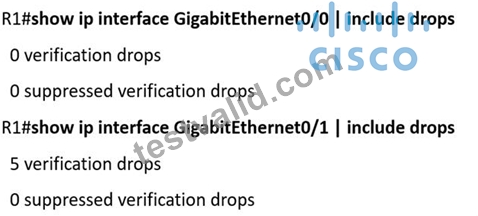
- A. Add a floating static route to the source on R1 to the GigabitEthernet 0/1 interface
- B. Remove the access list from the interface GigabrtEthernet 0/0
- C. Enable Cisco Express Forwarding to ensure that uRPF is functioning correctly
- D. Modify the uRPF mode from strict to loose
Answer: D
NEW QUESTION # 420
Refer to the exhibit.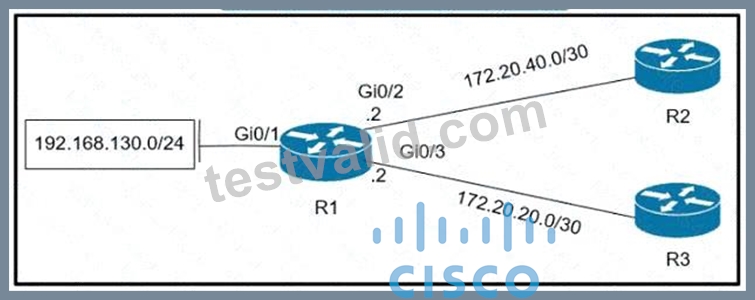
Which policy configuration on R1 forwards any traffic that is sourced from the 192 168 130 0'24 network to R2?
- A.
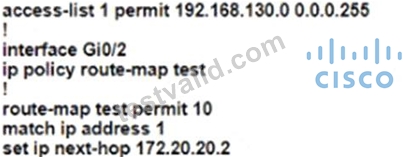
- B.
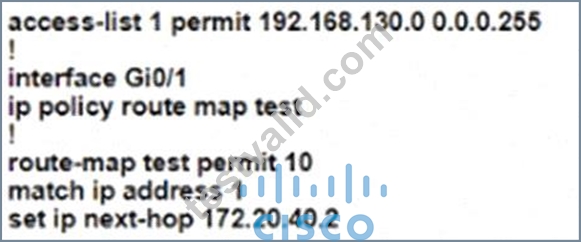
- C.
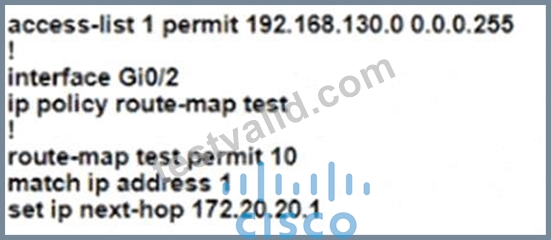
- D.
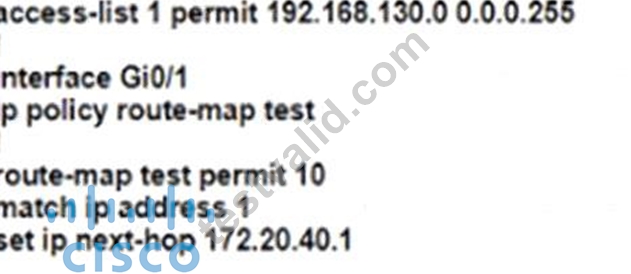
Answer: D
NEW QUESTION # 421
Refer to Exhibit. Which two configurations allow clients to get dynamic ip addresses assigned?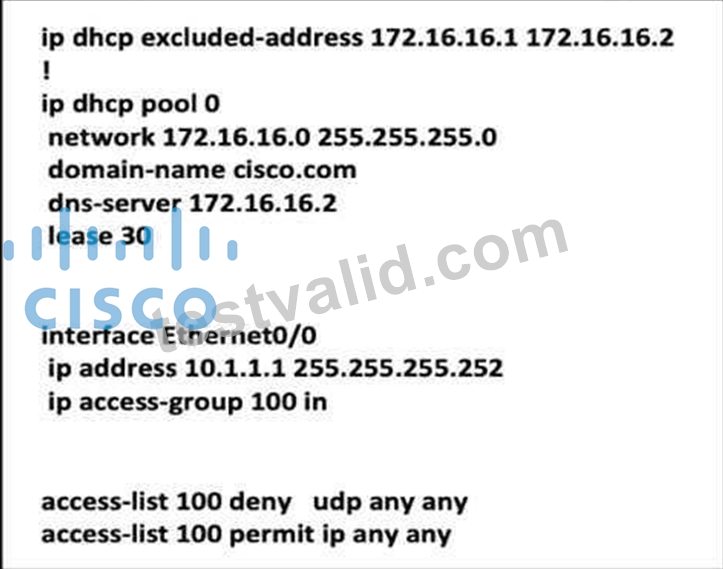
- A. Configure access-list 100 permit udp any any eq 69 as the first line
- B. Configure access-list 100 permit udp any any eq 68 as the first line
- C. Configure access-list 100 permit udp any any eq 86 as the first line
- D. Configure access-list 100 permit udp any any eq 67 as the first line
- E. Configure access-list 100 permit udp any any eq 61 as the first line
Answer: B,D
Explanation:
A DHCP server that receives a DHCPDISCOVER message may respond with a DHCPOFFER
message on UDP port 68 (BootP client).
...
In the event that the DHCP server is not on the local subnet, the DHCP server will send the
DHCPOFFER, as a unicast packet, on UDP port 67, back to the DHCP/BootP Relay Agent from
which the DHCPDISCOVER came.
Reference: https://www.cisco.com/c/en/us/support/docs/ip/dynamic-address-allocation-
resolution/27470-100.html
NEW QUESTION # 422
Refer to Exhibit.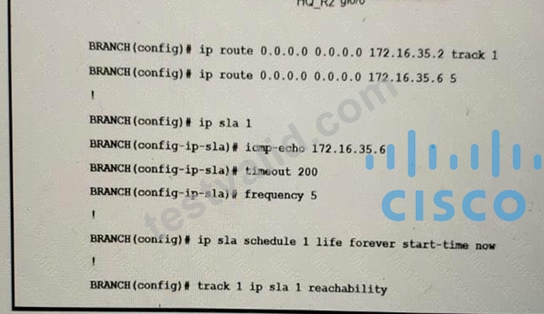
Traffic from the branch network should route through HQ R1 unless the path is unavailable. An engineer tests this functionality by shutting down interface on the BRANCH router toward HQ_R1 router but
192.168.20.0/24 is no longer reachable from the branch router. Which set of configurations resolves the issue?
- A. BRANCH(config)# ip sla 1
BRANCH(config-ip-sla)# icmp-echo 172.16.35.2 - B. HQ_R1(config)# ip sla responder
HQ_R1(config)# ip sla responder icmp-echo 172.16.35.2 - C. BRANCH(config)# ip sla 1
BRANCH(config-ip-sla)# icmp-echo 172.16.35.1 - D. HQ_R2(config)# ip sla responder
HQ_R2(config)# ip sla responder icmp-echo 172.16.35.5
Answer: A
Explanation:
In the configuration above, the engineer has made a mistake as he was tracking 172.16.35.6 (the backup path) instead of tracking the main path (172.16.35.2). Therefore,when he shut down the main path, the track 1 was still up so traffic still went through the main path -> it failed.
To fix this issue, we just need to correct the tracking interface of the main path.
NEW QUESTION # 423
A network administrator cannot connect to a device via SSH. The line vty configuration is as follows: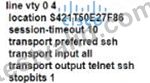
Which action resolves this issue?
- A. initialize the SSH key
- B. Change the stopbits to 10.
- C. Increase the session timeout
- D. Configure the transport input SSH
Answer: A
NEW QUESTION # 424
Refer to the exhibit. Routers R1 and R2 have established a network adjacency using EIGRP, and
both routers are advertising subnets to its neighbor. After issuing the show ip EIGRP topology all-
links command in R1, some prefixes are not showing R2 as a successor. Which action resolves
the issue?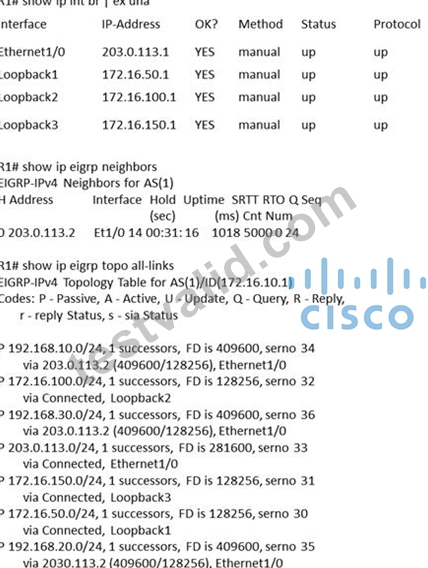
- A. Rectify the incorrect router ID in R2.
- B. Enable split-horizon.
- C. Configure the network statement on the neighbor.
- D. Resolve the incorrect metric on the link.
Answer: D
NEW QUESTION # 425
Refer to the exhibit.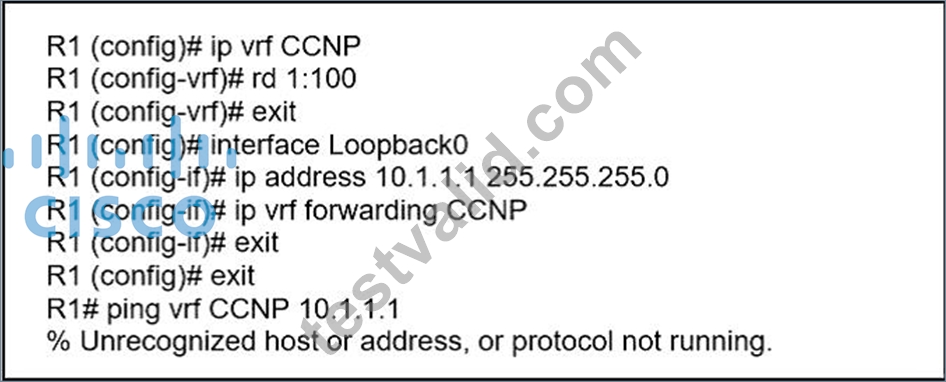
Which command must be configured to make VRF CCNP work?
- A. interface Loopback0
vrf forwarding CCNP - B. interface Loopback0
ip address 10.1.1.1 255.255.255.0 - C. interface Loopback0
ip address 10.1.1.1 255.255.255.0
vrf forwarding CCNP - D. interface Loopback0
ip address 10.1.1.1 255.255.255.0
ip vrf forwarding CCNP
Answer: B
Explanation:
From the exhibit, we learn that the command "ip address 10.1.1.1 255.255.255.0" has been issued before the command "ip vrf forwarding CCNP". But the second command removed the IP address configured in the first command so we have to retype the IP address command.
NEW QUESTION # 426
Refer to the exhibit.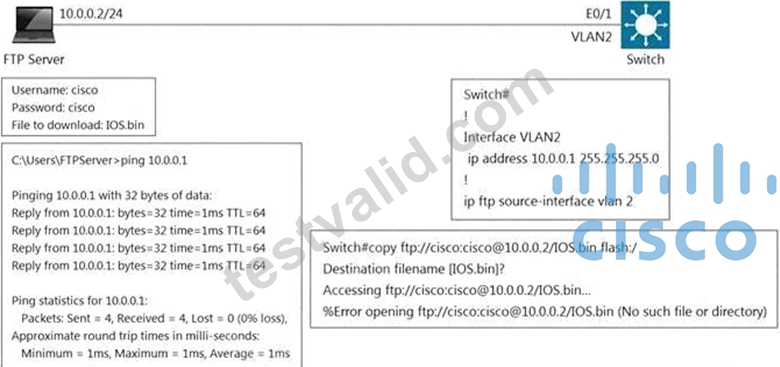
An engineer cannot copy the IOS.bin file from the FTP server to the switch.
Which action resolves the issue?
- A. Add the IOS.bin file, which does not exist on FTP server.
- B. Use the copy flash:/ ftp://[email protected]/IOS.bin command.
- C. Allow file permissions to download the file from the FTP server.
- D. Make memory space on the switch flash or USB drive to download the file.
Answer: A
NEW QUESTION # 427
Drag and drop the packet types from the left onto the correct descriptions on the right.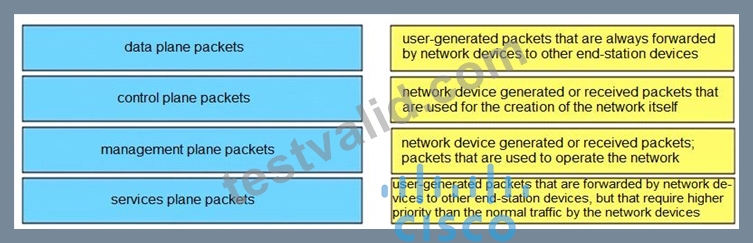
Answer:
Explanation: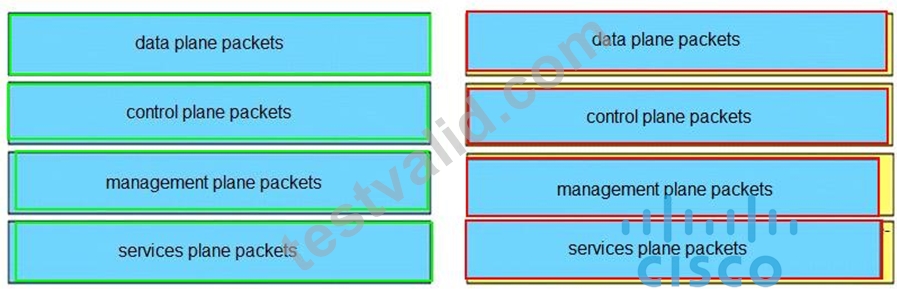
NEW QUESTION # 428
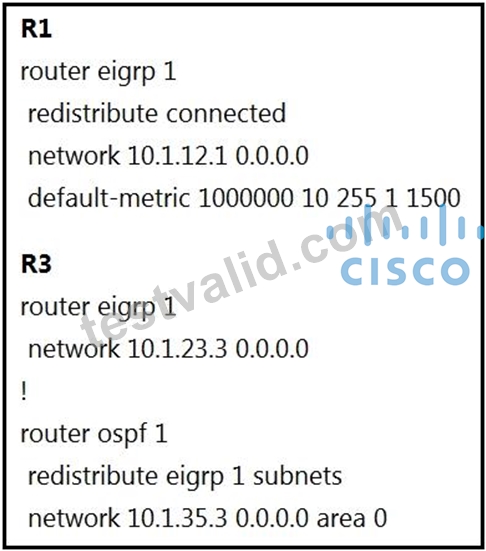
Refer to the exhibits. To provide reachability to network 10.1.1.0/24 from R5, the network
administrator redistributes EIGRP into OSPF on R3 but notices that R4 is now taking a
suboptimal path through R5 to reach 10.1.1.0/24 network.
Which action fixes the issue while keeping the reachability from R5 to 10.1.1.0/24 network?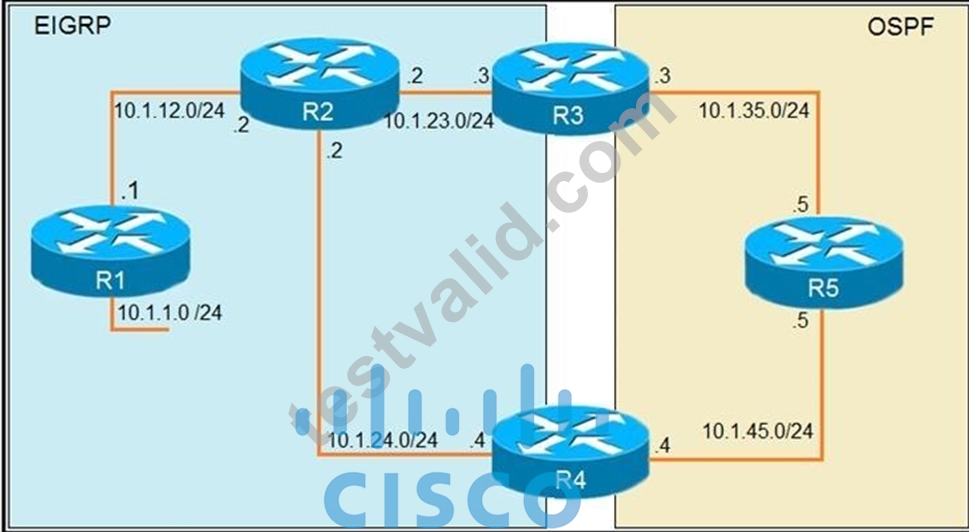
- A. Change the administrative distance of the external EIGRP to 90.
- B. Change the administrative distance of OSPF to 200 on R5.
- C. Apply the outbound distribution list on R5 toward R4 in OSPF.
- D. Redistribute OSPF into EIGRP on R4
Answer: A
Explanation:
The subnet 10.1.1.1/24 is redistributed into EIGRP domain so it will have the Administrative
Distance (AD) of 170. Therefore R4 also learns about this subnet advertised from R2 with the
same AD of 170.
In the other hand, subnet 10.1.1.0/24 is also redistributed into OSPF on R3 so R5 & R4 will learn
about this subnet with AD of 110, which is better than the above AD of 170 so R4 will choose
path R4 -> R5 -> R3 -> R2 -> R1.
In order to solve this problem, we can configure an outbound distribute list on R5 to prevent (filter
out) this subnet from advertising to R4. Then R4 only has one way to reach R1, which is R4 -> R2
- > R1. But this method will remove the backup route so it is not the best solution.
Another solution is to reduce the AD of the external EIGRP to a value smaller than 110. This
method reserves the backup route in case of the main route fails -> This is the best solution. To
do this, we can use the following command on R4:
router eigrp 1
distance eigrp 90 91 //Changes the AD to 90 for internal EIGRP routes and changes the AD to 91
for EIGRP external routes
We tested this lab in GNS3 and you can read this lab here. This is the result when we type the
"distance eigrp ..." command above on R4:
R4#show ip route
Gateway of last resort is not set
10.0.0.0/24 is subnetted, 6 subnets
D 10.1.12.0 [90/30720] via 10.1.24.2, 00:00:05, FastEthernet0/0 D EX 10.1.1.0 [91/33280] via
10.1.24.2, 00:00:05, FastEthernet0/0 C 10.1.24.0 is directly connected, FastEthernet0/0
D 10.1.23.0 [90/30720] via 10.1.24.2, 00:00:05, FastEthernet0/0 C 10.1.45.0 is directly
connected, FastEthernet1/0
O 10.1.35.0 [110/2] via 10.1.45.5, 00:00:11, FastEthernet1/0
Note: We can change the AD of EIGRP routes via the "distance eigrp ..." command but the effect
of this command is local only.
NEW QUESTION # 429
A company Is redesigning WAN infrastructure so that all branch sites must communicate via the head office and the head office can directly communicate with each site independently. The network engineer must configure the head office router by considering zero-touch technology when adding new sites in the same WAN infrastructure. Which configuration must be applied to the head office router to meet this requirement?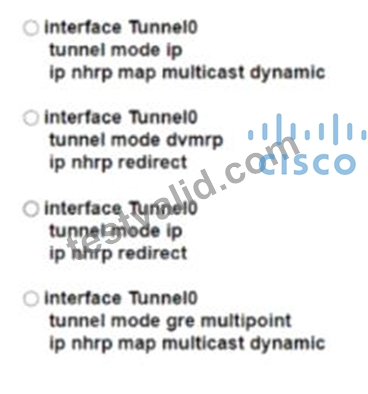
- A. Option B
- B. Option D
- C. Option A
- D. Option C
Answer: B
NEW QUESTION # 430
Drag and drop the MPLS terms from the left onto the correct definitions on the right.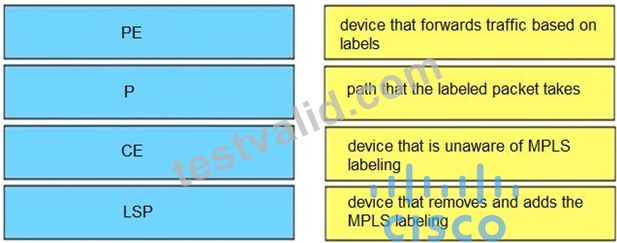
Answer:
Explanation: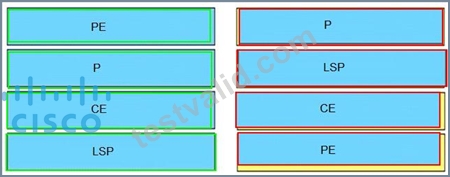
NEW QUESTION # 431
Refer to the exhibit.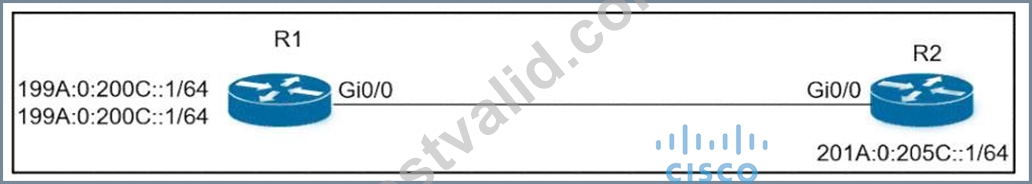
Which configuration denies Telnet traffic to router 2 from 198A:0:200C::1/64?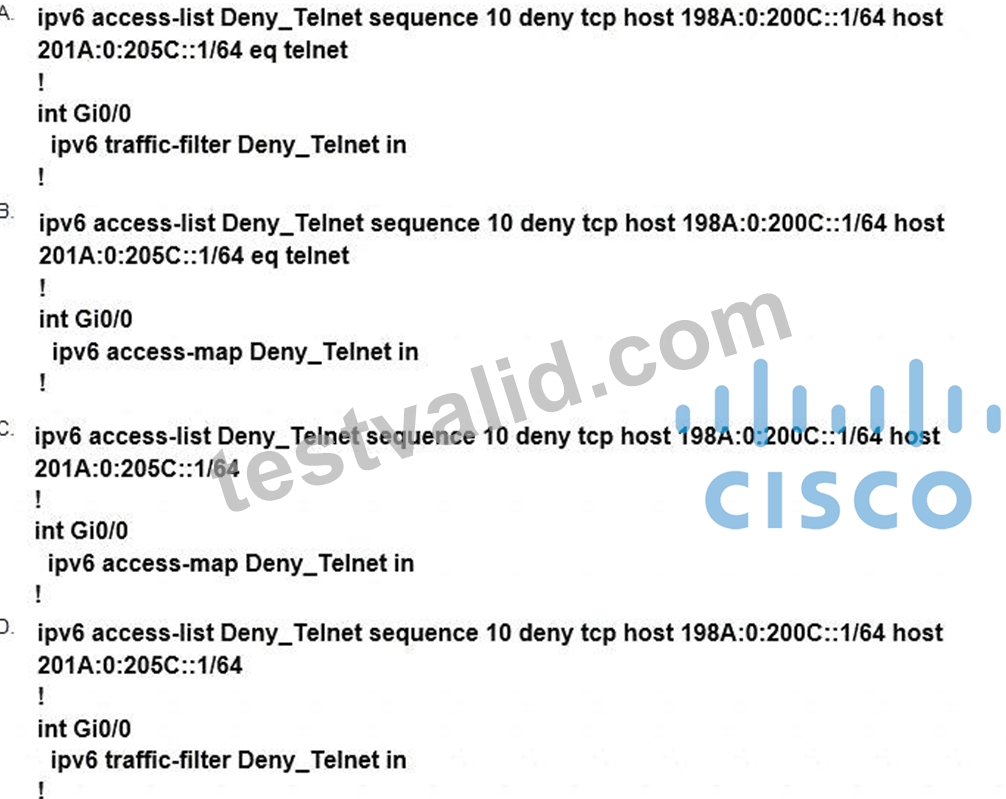
- A. Option B
- B. Option A
- C. Option D
- D. Option C
Answer: B
NEW QUESTION # 432
Drag and drop the MPLS VPN concepts from the left onto the correct descriptions on the right.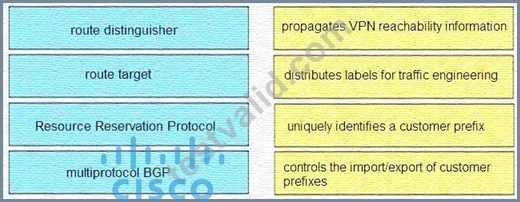
Answer:
Explanation: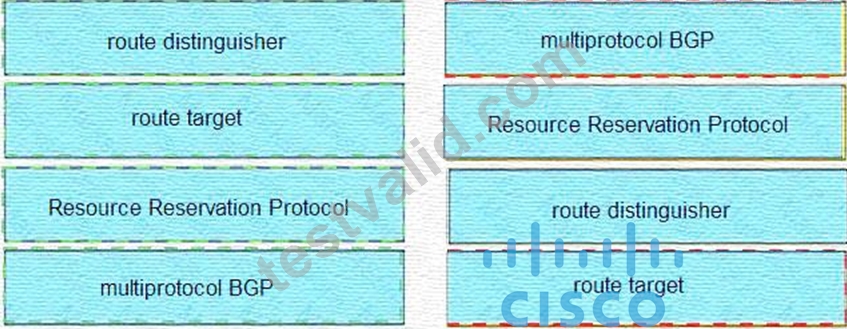
Explanation: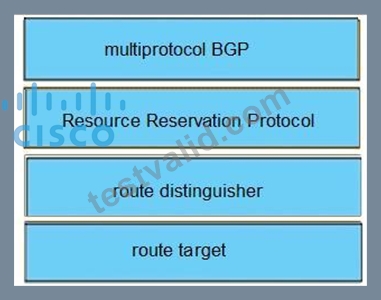
Reference:
https://www.rogerperkin.co.uk/featured/route-distinguisher-vs-route-target/
NEW QUESTION # 433
Refer to the exhibit. R1 is configured with uRPF, and ping to R1 is failing from a source present in the R1 routing table via the GigatxtEthernet 0/0 interface. Which action resolves the issue?
- A. Add a floating static route to the source on R1 to the GigabitEthernet 0/1 interface
- B. Remove the access list from the interface GigabrtEthernet 0/0
- C. Enable Cisco Express Forwarding to ensure that uRPF is functioning correctly
- D. Modify the uRPF mode from strict to loose
Answer: D
NEW QUESTION # 434
Which protocol does MPLS use to support traffic engineering?
- A. Label Distribution Protocol (LDP)
- B. Tag Distribution Protocol (TDP)
- C. Border Gateway Protocol (BGP)
- D. Resource Reservation Protocol (RSVP)
Answer: D
Explanation:
NEW QUESTION # 435
Refer to the exhibit.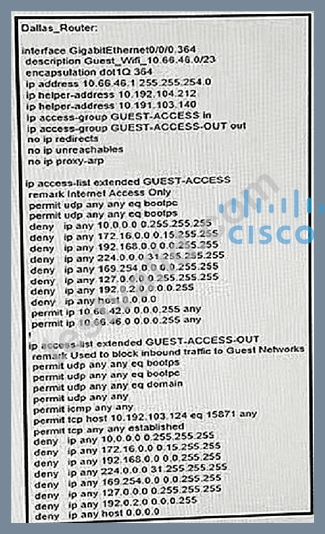
After a new regional office is set up,not all guests can access the internet via guest Wi Fi. Clients are getting the correct IP address from guest Wi-Fi VLAN 364. which action resolves the issue ?
- A. Allow DNS traffic through the inbound ACL
- B. Allow 10.66.46.0/23 in the inbound ACL
- C. Allow DNS traffic through the outbound ACL
- D. Allow 10.66.46.0/23 in the outbound ACL
Answer: A
NEW QUESTION # 436
Refer to the exhibit. An administrator that is connected to the console does not see debug messages when remote users log in.
Which action ensures that debug messages are displayed for remote logins?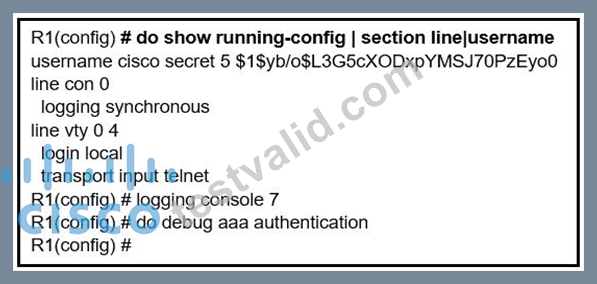
- A. Enter the transport input ssh configuration command.
- B. Enter the terminal monitor exec command.
- C. Enter the aaa new-model configuration command.
- D. Enter the logging console debugging configuration command.
Answer: C
Explanation:
To enable AAA, you need to configure the aaa new-model command in global configuration.
Note: Until this command is enabled, all other AAA commands are hidden.
Warning: The aaa new-model command immediately applies local authentication to all lines and interfaces (except console line line con 0). If a telnet session is opened to the router after enabling this command (or if a connection times out and has to reconnect), then the user has to be authenticated using the the local database of the router. To avoid being locked out of the router, we recommend that you define a username and password on the access server before starting the AAA configuration.
https://www.cisco.com/c/en/us/support/docs/security-vpn/terminal-access-controller-access- control-system-tacacs-/10384-security.html
NEW QUESTION # 437 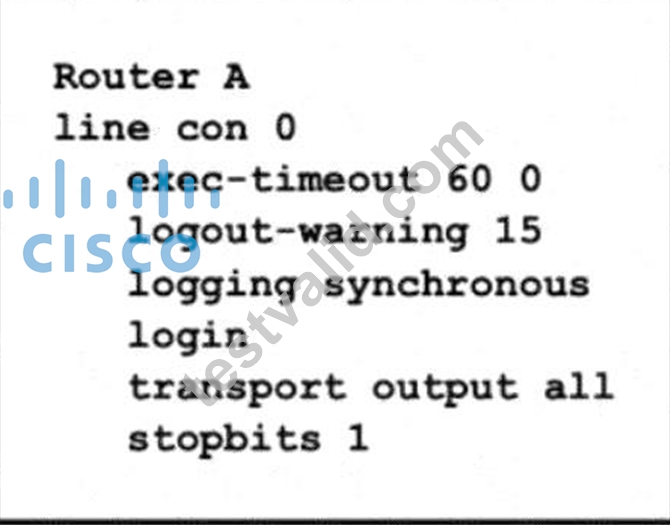
Refer to the exhibit After a misconfiguration by a junior engineer, the console access to router A is not working Which configuration allows access to router A?
A)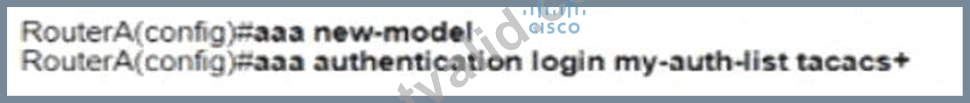
B)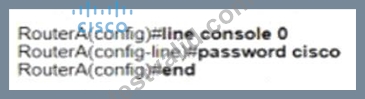
C)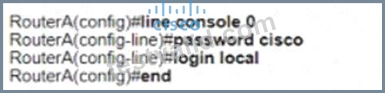
D)
- A. Option C
- B. Option B
- C. Option A
- D. Option D
Answer: A
NEW QUESTION # 438 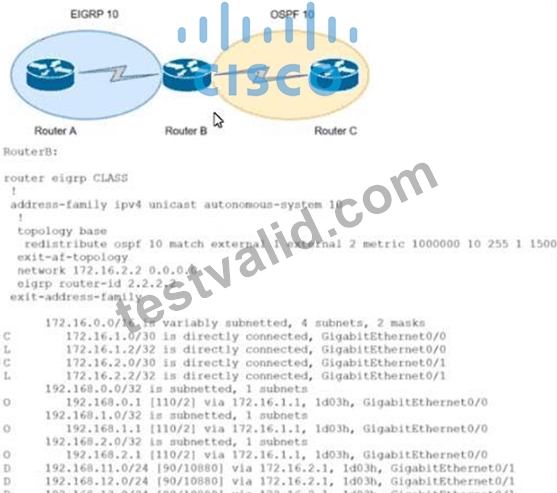
Refer to the exhibit. An engineer configured route exchange between two different companies for a migration project EIGRP routes were learned in router C but no OSPF routes were learned in router A. Which configuration allows router A to receive OSPF routes?
- A. (config-router-af)#redistribute ospf 10 1000000 10 255 1 1500
- B. (config-router-af-topology)#redistribute connected
- C. (config-routeraf-topology)#redistribute ospf 10 metric 1000000 10 255 1 1500
- D. (config-router-af-topology )#no redistribute ospf 10 match external 1 external 2 metric 1000000 10 255
1 1500
Answer: C
NEW QUESTION # 439
Refer to the exhibit.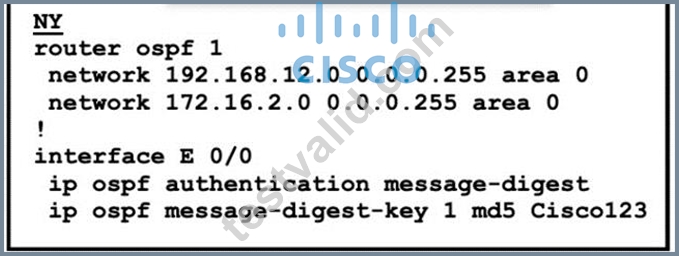
The neighbor relationship is not coming up Which two configurations bring the adjacency up? (Choose two)
- A. LA
interface E 0/0
ip ospf authentication-key Cisco123 - B. NY
router ospf 1
area 0 authentication message-digest - C. NY
interface E 0/0
no ip ospf message-digest-key 1 md5 Cisco123
ip ospf authentication-key Cisco123 - D. LA
router ospf 1
area 0 authentication message-digest - E. LA
interface E 0/0
ip ospf message-digest-key 1 md5 Cisco123
Answer: D,E
NEW QUESTION # 440
Refer to the exhibit.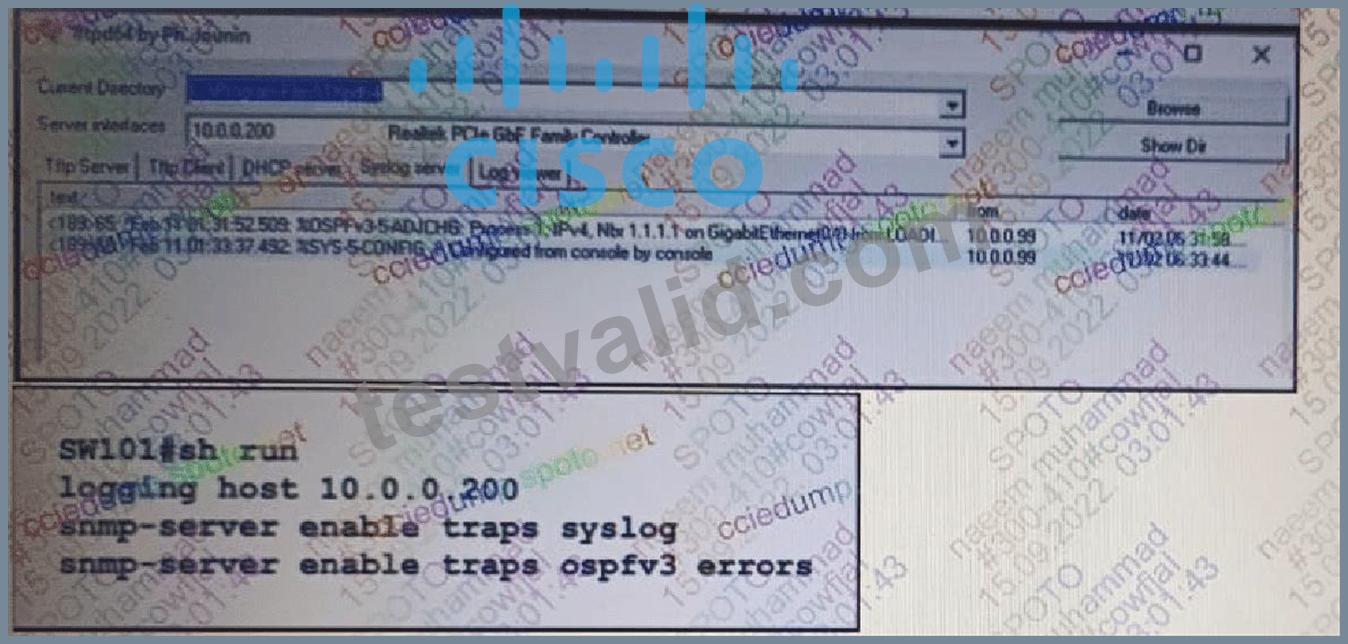
An engineer configures SW101 to send OSPFv3 interfaces state change messages to the server. However, only some OSPFv3 errors are being recorded. which organization resolves the ..?
- A. snmp-server-enable traps ospfv3 state-change neighbor-state-change.
- B. snmp-server-enable traps ospfv3 state-change if-state-change neighbor-state-change
- C. snmp-server-enable traps ospfv3 state-change restart-status-change
- D. snmp-server enable traps ospfv3 state-change if-state-change
Answer: B
NEW QUESTION # 441
Refer to the exhibit. After a security hardening was performed on a router, the administrator cannot access the command line of any remote device. Which action resolves the issue?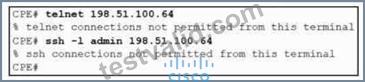
- A. Remove the egress ACL blocking Telnet and SSH on the router interfaces.
- B. Remove the transport output none command from the line con 0 section.
- C. Move Telnet and SSH commands to a nonzero privilege level.
- D. Modify the AAA policy to allow the user to run the Telnet and SSH commands.
Answer: A
NEW QUESTION # 442
Refer to the exhibit.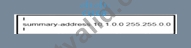
The none area 0 routers in OSPF still receive more specific routes of 10.1.1.0.10.1.2.0.10.1.3.0 from area
0. Which action resolves the issue?
- A. Summarize by using the summary-address 10.1.0.0 255.255.252.0 command.
- B. Configure route summarization on OSPF-enabled interfaces.
- C. Summarize by using the area range command on ABRs
- D. Configure the summary-address 10.1.0.0 255.255.252.0 command under OSPF process.
Answer: C
NEW QUESTION # 443
Refer to the exhibit.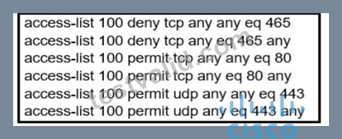
During troubleshooting it was discovered that the device is not reachable using a secure web browser.
What is needed to fix the problem?
- A. permit tcp port 443
- B. permit udp port 465
- C. permit tcp port 465.
- D. permit tcp port 22
Answer: A
NEW QUESTION # 444
......
Cisco 300-410 exam is ideal for network professionals who want to enhance their knowledge and skills in enterprise networking. 300-410 exam validates the ability of candidates to implement complex routing solutions using advanced technologies such as BGP, OSPF, and EIGRP. It also tests the candidate's ability to implement VPN technologies such as DMVPN and FlexVPN.
Cisco 300-410 exam is intended for professionals who have a strong understanding of networking technologies and experience in implementing and managing enterprise networks. Candidates should have a solid understanding of routing protocols such as OSPF, EIGRP, and BGP, as well as the ability to configure and troubleshoot network services such as NAT, DHCP, and VPNs. Additionally, candidates should have experience with network automation tools and techniques, as well as the ability to design and implement highly available and scalable network solutions. Passing the Cisco 300-410 exam is a valuable achievement for IT professionals who are seeking to advance their careers in enterprise networking.
Download 300-410 Exam Dumps Questions to get 100% Success: https://pass4sure.testvalid.com/300-410-valid-exam-test.html