

[Mar-2024] Vault-Associate Dumps With 100% Verified Q&As - Pass Guarantee or Full Refund
Pass HashiCorp Vault-Associate Exam With Practice Test Questions Dumps Bundle
HashiCorp Vault-Associate Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
NEW QUESTION # 12
Your DevOps team would like to provision VMs in GCP via a CICD pipeline. They would like to integrate Vault to protect the credentials used by the tool. Which secrets engine would you recommend?
- A. Google Cloud Secrets Engine
- B. Identity secrets engine
- C. Key/Value secrets engine version 2
- D. SSH secrets engine
Answer: A
Explanation:
The Google Cloud Secrets Engine is the best option for the DevOps team to provision VMs in GCP via a CICD pipeline and integrate Vault to protect the credentials used by the tool. The Google Cloud Secrets Engine can dynamically generate GCP service account keys or OAuth tokens based on IAM policies, which can be used to authenticate and authorize the CICD tool to access GCP resources. The credentials are automatically revoked when they are no longer used or when the lease expires, ensuring that the credentials are short-lived and secure. The DevOps team can configure rolesets or static accounts in Vault to define the scope and permissions of the credentials, and use the Vault API or CLI to request credentials on demand. The Google Cloud Secrets Engine also supports generating access tokens for impersonated service accounts, which can be useful for delegating access to other service accounts without storing or managing their keys1.
The Identity Secrets Engine is not a good option for this use case, because it does not generate GCP credentials, but rather generates identity tokens that can be used to access other Vault secrets engines or namespaces2. The Key/Value Secrets Engine version 2 is also not a good option, because it does not generate dynamic credentials, but rather stores and manages static secrets that the user provides3. The SSH Secrets Engine is not a good option either, because it does not generate GCP credentials, but rather generates SSH keys or OTPs that can be used to access remote hosts via SSH4.
Reference:
Google Cloud - Secrets Engines | Vault | HashiCorp Developer
Identity - Secrets Engines | Vault | HashiCorp Developer
KV - Secrets Engines | Vault | HashiCorp Developer
SSH - Secrets Engines | Vault | HashiCorp Developer
NEW QUESTION # 13
Which of these are a benefit of using the Vault Agent?
- A. Vault Agent will manage the lifecycle of cached tokens and leases automatically
- B. Vault Agent will enforce minimum levels of encryption an application can use
- C. Vault Agent will auto-discover which authentication mechanism to use
- D. Vault Agent allows for centralized configuration of application secrets engines
Answer: A
Explanation:
Vault Agent is a client daemon that provides the following features:
Auto-Auth - Automatically authenticate to Vault and manage the token renewal process for locally-retrieved dynamic secrets.
API Proxy - Allows Vault Agent to act as a proxy for Vault's API, optionally using (or forcing the use of) the Auto-Auth token.
Caching - Allows client-side caching of responses containing newly created tokens and responses containing leased secrets generated off of these newly created tokens. The agent also manages the renewals of the cached tokens and leases.
Templating - Allows rendering of user-supplied templates by Vault Agent, using the token generated by the Auto-Auth step.
Process Supervisor Mode - Runs a child process with Vault secrets injected as environment variables.
One of the benefits of using the Vault Agent is that it will manage the lifecycle of cached tokens and leases automatically. This means that the agent will handle the token renewal and revocation logic, as well as the lease renewal and revocation logic for the secrets that are cached by the agent. This reduces the burden on the application developers and operators, and ensures that the tokens and secrets are always valid and up-to-date. Reference: Vault Agent | Vault | HashiCorp Developer, Caching - Vault Agent | Vault | HashiCorp Developer
NEW QUESTION # 14
You are performing a high number of authentications in a short amount of time. You're experiencing slow throughput for token generation. How would you solve this problem?
- A. Reduce the number of policies attached to the tokens
- B. Establish a rate limit quota
- C. Implement batch tokens
- D. Increase the time-to-live on service tokens
Answer: C
Explanation:
Batch tokens are a type of tokens that are not persisted in Vault's storage backend, but are encrypted blobs that carry enough information to perform Vault actions. Batch tokens are extremely lightweight and scalable, and can improve the throughput for token generation. Batch tokens are suitable for high-volume and ephemeral workloads, such as containers or serverless functions, that require short-lived and non-renewable tokens. Batch tokens can be created by using the -type=batch flag in the vault token create command, or by configuring the token_type parameter in the auth method's role or mount options. Batch tokens have some limitations compared to service tokens, such as the lack of renewal, revocation, listing, accessor, and cubbyhole features. Therefore, batch tokens should be used with caution and only when the trade-offs are acceptable. Reference: https://developer.hashicorp.com/vault/tutorials/tokens/batch-tokens1, https://developer.hashicorp.com/vault/docs/commands/token/create2, https://developer.hashicorp.com/vault/docs/concepts/tokens#token-types3
NEW QUESTION # 15
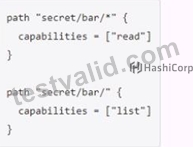
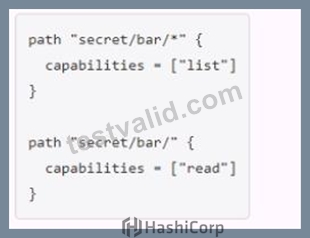
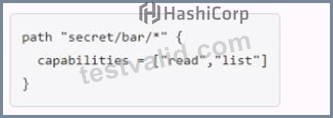
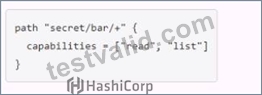
You have been tasked with writing a policy that will allow read permissions for all secrets at path secret/bar. The users that are assigned this policy should also be able to list the secrets. What should this policy look like?
- A.
- B.
- C.
- D.
Answer: A
Explanation:
This policy would allow read permissions for all secrets at path secret/bar, as well as list permissions for the secret/bar/ path. The list permission is required to be able to see the names of the secrets under a given path1. The wildcard () character matches any number of characters within a single path segment, while the slash (/) character matches the end of the path2. Therefore, the policy would grant read access to any secret that starts with secret/bar/, such as secret/bar/foo or secret/bar/baz, but not to secret/bar itself. To grant list access to secret/bar, the policy needs to specify the exact path with a slash at the end. This policy follows the principle of least privilege, which means that it only grants the minimum permissions necessary for the users to perform their tasks3.
The other options are not correct because they either grant too much or too little permissions. Option A would grant both read and list permissions to all secrets under secret/bar, which is more than what is required. Option B would grant list permissions to all secrets under secret/bar, but only read permissions to secret/bar itself, which is not what is required. Option D would use an invalid character (+) in the policy, which would cause an error.
Reference:
Policy Syntax | Vault | HashiCorp Developer
Policy Syntax | Vault | HashiCorp Developer
Policies | Vault | HashiCorp Developer
NEW QUESTION # 16
Use this screenshot to answer the question below: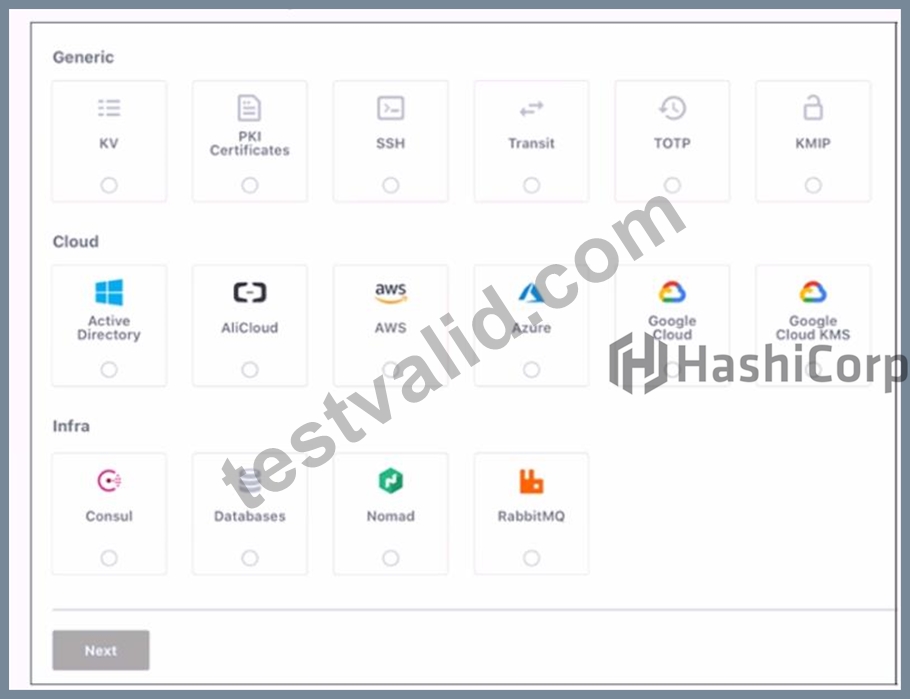
When are you shown these options in the GUI?
- A. Enabling authentication methods
- B. Enabling policies
- C. Enabling secret engines
- D. Enabling authentication engines
Answer: A
Explanation:
This screenshot is shown when you are enabling authentication methods in the GUI. Authentication methods are the ways users and applications authenticate with Vault. Vault supports many different authentication methods, including username and password, GitHub, and more. You can enable one or more authentication methods from the grid of options, which are divided into three categories: Generic, Cloud, and Infra. Each option has a name, a description, and a logo. You can also enable authentication methods using the Vault CLI or API.
Enabling policies, authentication engines, and secret engines are different tasks that are not related to this screenshot. Policies are rules that govern the access to Vault resources, such as secrets, authentication methods, and audit devices. Authentication engines are components of Vault that perform authentication and assign policies to authenticated entities. Secret engines are components of Vault that store, generate, or encrypt data. These tasks have different GUI pages and options than the screenshot.
Reference:
[Authentication | Vault | HashiCorp Developer]
[Policies | Vault | HashiCorp Developer]
[Authentication | Vault | HashiCorp Developer]
[Secrets Engines | Vault | HashiCorp Developer]
NEW QUESTION # 17
Which of these is not a benefit of dynamic secrets?
- A. Replaces cumbersome password rotation tools and practices
- B. Minimizes damage of credentials leaking
- C. Ensures that administrators can see every password used
- D. Supports systems which do not natively provide a method of expiring credentials
Answer: C
Explanation:
Dynamic secrets are generated on-demand by Vault and have a limited time-to-live (TTL). They do not ensure that administrators can see every password used, as they are often encrypted and ephemeral. The benefits of dynamic secrets are:
They support systems that do not natively provide a method of expiring credentials, such as databases, cloud providers, SSH, etc. Vault can revoke the credentials when they are no longer needed or when the lease expires.
They minimize the damage of credentials leaking, as they are short-lived and can be easily rotated or revoked. If a credential is compromised, the attacker has a limited window of opportunity to use it before it becomes invalid.
They replace cumbersome password rotation tools and practices, as Vault can handle the generation and revocation of credentials automatically and securely. This reduces the operational overhead and complexity of managing secrets.
NEW QUESTION # 18
When using Integrated Storage, which of the following should you do to recover from possible data loss?
- A. Use audit logs
- B. Use snapshot
- C. Failover to a standby node
- D. Use server logs
Answer: B
Explanation:
Integrated Storage is a Raft-based storage backend that allows Vault to store its data internally without relying on an external storage system. It also enables Vault to run in high availability mode with automatic leader election and failover. However, Integrated Storage is not immune to data loss or corruption due to hardware failures, network partitions, or human errors. Therefore, it is recommended to use the snapshot feature to backup and restore the Vault data periodically or on demand. A snapshot is a point-in-time capture of the entire Vault data, including the encrypted secrets, the configuration, and the metadata. Snapshots can be taken and restored using the vault operator raft snapshot command or the sys/storage/raft/snapshot API endpoint. Snapshots are encrypted and can only be restored with a quorum of unseal keys or recovery keys. Snapshots are also portable and can be used to migrate data between different Vault clusters or storage backends. Reference: https://developer.hashicorp.com/vault/docs/concepts/integrated-storage1, https://developer.hashicorp.com/vault/docs/commands/operator/raft/snapshot2, https://developer.hashicorp.com/vault/api-docs/system/storage/raft/snapshot3
NEW QUESTION # 19
The Vault encryption key is stored in Vault's backend storage.
- A. True
- B. False
Answer: B
Explanation:
The statement is false. The Vault encryption key is not stored in Vault's backend storage, but rather in Vault's memory. The Vault encryption key is the key that is used to encrypt and decrypt the data that is stored in Vault's backend storage, such as secrets, tokens, policies, etc. The Vault encryption key is derived from the master key, which is generated when Vault is initialized. The master key is split into unseal keys using Shamir's secret sharing algorithm, and the unseal keys are distributed to trusted operators. To start Vault, a quorum of unseal keys is required to reconstruct the master key and derive the encryption key. The encryption key is then kept in memory and used to protect the data in Vault's backend storage. The encryption key is never written to disk or exposed via the API. Reference: Seal/Unseal | Vault | HashiCorp Developer, Key Rotation | Vault | HashiCorp Developer
NEW QUESTION # 20
Which of the following statements describe the secrets engine in Vault? Choose three correct answers.
- A. Once enabled, you cannot disable the secrets engine
- B. Some secrets engines simply store and read data
- C. Each secrets engine is isolated to its path
- D. You can build your own custom secrets engine
- E. A secrets engine cannot be enabled at multiple paths
Answer: B,C,D
Explanation:
Secrets engines are components that store, generate, or encrypt data in Vault. They are enabled at a specific path in Vault and have their own API and configuration. Some of the statements that describe the secrets engines in Vault are:
Some secrets engines simply store and read data, such as the key/value secrets engine, which acts like an encrypted Redis or Memcached. Other secrets engines perform more complex operations, such as generating dynamic credentials, encrypting data, issuing certificates, etc1.
You can build your own custom secrets engine by using the plugin system, which allows you to write and run your own secrets engine as a separate process that communicates with Vault over gRPC. You can also use the SDK to create your own secrets engine in Go and compile it into Vault2.
Each secrets engine is isolated to its path, which means that the secrets engine cannot access or interact with other secrets engines or data outside its path. The path where the secrets engine is enabled can be customized and can have multiple segments. For example, you can enable the AWS secrets engine at aws/ or aws/prod/ or aws/dev/3.
The statements that are not true about the secrets engines in Vault are:
You can disable an existing secrets engine by using the vault secrets disable command or the sys/mounts API endpoint. When a secrets engine is disabled, all of its secrets are revoked and all of its data is deleted from the storage backend4.
A secrets engine can be enabled at multiple paths, with a few exceptions, such as the system and identity secrets engines. Each secrets engine enabled at a different path is independent and isolated from others. For example, you can enable the KV secrets engine at kv/ and secret/ and they will not share any data3.
NEW QUESTION # 21
You are using Vault's Transit secrets engine to encrypt your dat
a. You want to reduce the amount of content encrypted with a single key in case the key gets compromised. How would you do this?
- A. Periodically re-key the Vault's unseal keys
- B. Periodically rotate the encryption key
- C. Use 4096-bit RSA key to encrypt the data
- D. Upgrade to Vault Enterprise and integrate with HSM
Answer: B
Explanation:
The Transit secrets engine supports the rotation of encryption keys, which allows you to change the key that is used to encrypt new data without affecting the ability to decrypt data that was already encrypted. This reduces the amount of content encrypted with a single key in case the key gets compromised, and also helps you comply with the NIST guidelines for key rotation. You can rotate the encryption key manually by invoking the /transit/keys/<name>/rotate endpoint, or you can configure the key to automatically rotate based on a time interval or a number of encryption operations. When you rotate a key, Vault generates a new key version and increments the key's latest_version metadata. The new key version becomes the encryption key used for encrypting any new data. The previous key versions are still available for decrypting the existing data, unless you specify a minimum decryption version to archive the old key versions. You can also delete or disable old key versions if you want to revoke access to the data encrypted with those versions. Reference: https://developer.hashicorp.com/vault/docs/secrets/transit1, https://developer.hashicorp.com/vault/api-docs/secret/transit2
NEW QUESTION # 22
A user issues the following cURL command to encrypt data using the transit engine and the Vault AP: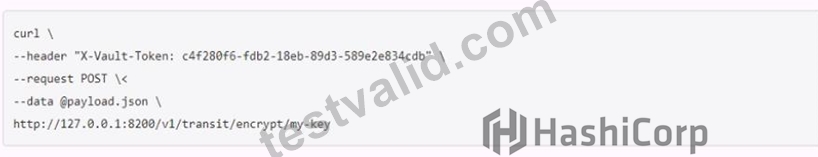
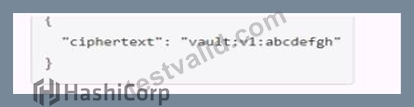
Which payload.json file has the correct contents?
- A.
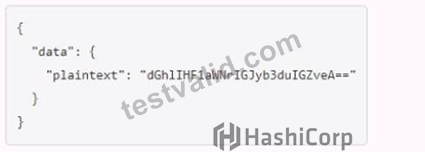
- B.
- C.
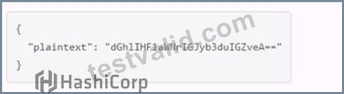
- D.
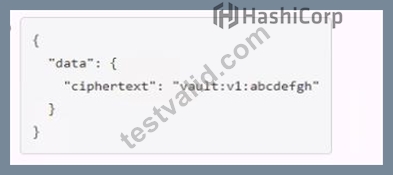
Answer: A
Explanation:
The payload.json file that has the correct contents is C. This file contains a JSON object with a single key, "plaintext", and a value that is the base64-encoded string of the data to be encrypted. This is the format that the Vault API expects for the transit encrypt endpoint1. The other files are not correct because they either have the wrong key name, the wrong value format, or the wrong JSON syntax.
Reference:
Encrypt Data - Transit Secrets Engine | Vault | HashiCorp Developer
NEW QUESTION # 23
The following three policies exist in Vault. What do these policies allow an organization to do?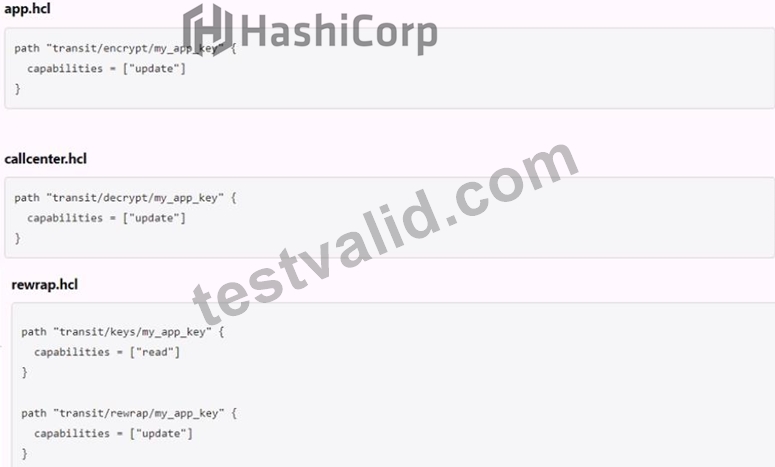
- A. Separates permissions allowed on actions associated with the transit secret engine
- B. Create a transit encryption key for encrypting, decrypting, and rewrapping encrypted data
- C. Nothing, as the minimum permissions to perform useful tasks are not present
- D. Encrypt, decrypt, and rewrap data using the transit engine all in one policy
Answer: D
Explanation:
The three policies that exist in Vault are:
admins: This policy grants full access to all secrets and operations in Vault. It can be used by administrators or operators who need to manage all aspects of Vault.
default: This policy grants access to all secrets and operations in Vault except for those that require specific policies. It can be used as a fallback policy when no other policy matches.
transit: This policy grants access only to the transit secrets engine, which handles cryptographic functions on data in-transit. It can be used by applications or services that need to encrypt or decrypt data using Vault.
These policies allow an organization to perform useful tasks such as:
Encrypting, decrypting, and rewrapping data using the transit engine all in one policy: This policy grants access to both the transit secrets engine and the default policy, which allows performing any operation on any secret in Vault.
Creating a transit encryption key for encrypting, decrypting, and rewrapping encrypted data: This policy grants access only to the transit secrets engine and its associated keys, which are used for encrypting and decrypting data in transit using AES-GCM with a 256-bit AES key or other supported key types.
Separating permissions allowed on actions associated with the transit secret engine: This policy grants access only to specific actions related to the transit secrets engine, such as creating keys or wrapping requests. It does not grant access to other operations or secrets in Vault.
NEW QUESTION # 24
When unsealing Vault, each Shamir unseal key should be entered:
- A. Sequentially from one system that all of the administrators are in front of
- B. While encrypted with each administrators PGP key
- C. By different administrators each connecting from different computers
- D. At the command line in one single command
Answer: C
Explanation:
When unsealing Vault, each Shamir unseal key should be entered by different administrators each connecting from different computers. This is because the Shamir unseal keys are split into shares that are distributed to trusted operators, and no single operator should have access to more than one share. This way, the unseal process requires the cooperation of a quorum of key holders, and enhances the security and availability of Vault. The unseal keys can be entered via multiple mechanisms from multiple client machines, and the process is stateful. The order of the keys does not matter, as long as the threshold number of keys is reached. The unseal keys should not be entered at the command line in one single command, as this would expose them to the history and compromise the security. The unseal keys should not be encrypted with each administrator's PGP key, as this would prevent Vault from decrypting them and reconstructing the master key. Reference: https://developer.hashicorp.com/vault/docs/concepts/seal3, https://developer.hashicorp.com/vault/docs/commands/operator/unseal
NEW QUESTION # 25
You can build a high availability Vault cluster with any storage backend.
- A. True
- B. False
Answer: B
Explanation:
Not all storage backends support high availability mode for Vault. Only the storage backends that support locking can enable Vault to run in a multi-server mode where one server is active and the others are standby. Some examples of storage backends that support high availability mode are Consul, Integrated Storage, and ZooKeeper. Some examples of storage backends that do not support high availability mode are Filesystem, MySQL, and PostgreSQL. Reference: https://developer.hashicorp.com/vault/docs/concepts/ha1, https://developer.hashicorp.com/vault/docs/configuration/storage2
NEW QUESTION # 26
The vault lease renew command increments the lease time from:
- A. The current time
- B. The end of the lease
Answer: A
Explanation:
The vault lease renew command increments the lease time from the current time, not the end of the lease. This means that the user can request a specific amount of time they want remaining on the lease, termed the increment. This is not an increment at the end of the current TTL; it is an increment from the current time. For example, vault lease renew -increment=3600 my-lease-id would request that the TTL of the lease be adjusted to 1 hour (3600 seconds) from now. Having the increment be rooted at the current time instead of the end of the lease makes it easy for users to reduce the length of leases if they don't actually need credentials for the full possible lease period, allowing those credentials to expire sooner and resources to be cleaned up earlier. The requested increment is completely advisory. The backend in charge of the secret can choose to completely ignore it1. Reference:
Lease, Renew, and Revoke | Vault | HashiCorp Developer
NEW QUESTION # 27
Running the second command in the GUI CLI will succeed.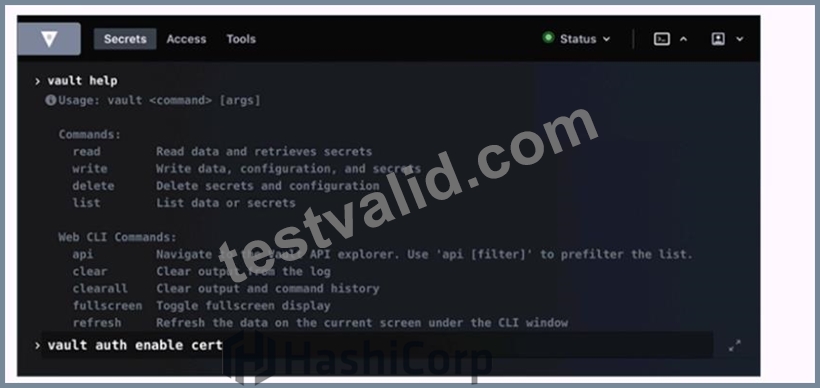
- A. True
- B. False
Answer: B
Explanation:
Running the second command in the GUI CLI will fail. The second command is vault kv put secret/creds passcode=my-long-passcode. This command attempts to write a secret named creds with the value passcode=my-long-passcode to the secret path, which is the default path for the kv secrets engine. However, the kv secrets engine is not enabled at the secret path, as shown by the first command vault secrets list, which lists the enabled secrets engines and their paths. The only enabled secrets engine is the transit secrets engine at the transit path. Therefore, the second command will fail with an error message saying that no secrets engine is mounted at the path secret/. To make the second command succeed, the kv secrets engine must be enabled at the secret path or another path, using the vault secrets enable command. For example, vault secrets enable -path=secret kv would enable the kv secrets engine at the secret path. Reference: kv - Command | Vault | HashiCorp Developer, vault secrets enable - Command | Vault | HashiCorp Developer
NEW QUESTION # 28
What is the Vault CLI command to query information about the token the client is currently using?
- A. vault token lookup
- B. vault self-lookup
- C. vault lookup self
- D. vault lookup token
Answer: A
Explanation:
The Vault CLI command to query information about the token the client is currently using is vault token lookup. This command displays information about the token or accessor provided as an argument, or the locally authenticated token if no argument is given. The information includes the token ID, accessor, policies, TTL, creation time, and metadata. This command can be useful for debugging and auditing purposes, as well as for renewing or revoking tokens. Reference: token lookup - Command | Vault | HashiCorp Developer, Tokens | Vault | HashiCorp Developer
NEW QUESTION # 29
To make an authenticated request via the Vault HTTP API, which header would you use?
- A. The Content-Type HTTP Header
- B. The X-Vault-Namespace HTTP Header
- C. The X-Vault-Token HTTP Header
- D. The x-Vault-Request HTTP Header
Answer: C
Explanation:
To make an authenticated request via the Vault HTTP API, you need to use the X-Vault-Token HTTP Header or the Authorization HTTP Header using the Bearer <token> scheme. The token is a string that represents your identity and permissions in Vault. You can obtain a token by using an authentication method, such as userpass, approle, aws, etc. The token can also be a root token, which has unlimited access to Vault, or a wrapped token, which is a response-wrapping token that can be used to unwrap the actual token. The token must be sent with every request to Vault that requires authentication, except for the unauthenticated endpoints, such as sys/init, sys/seal-status, sys/unseal, etc. The token is used by Vault to verify your identity and enforce the policies that grant or deny access to various paths and operations. Reference: https://developer.hashicorp.com/vault/api-docs3, https://developer.hashicorp.com/vault/docs/concepts/tokens4, https://developer.hashicorp.com/vault/docs/concepts/auth5
NEW QUESTION # 30
Where do you define the Namespace to log into using the Vault Ul?
To answer this question
Use your mouse to click on the screenshot in the location described above. An arrow indicator will mark where you have clicked. Click the "Answer" button once you have positioned the arrow to answer the question. You may need to scroll down to see the entire screenshot.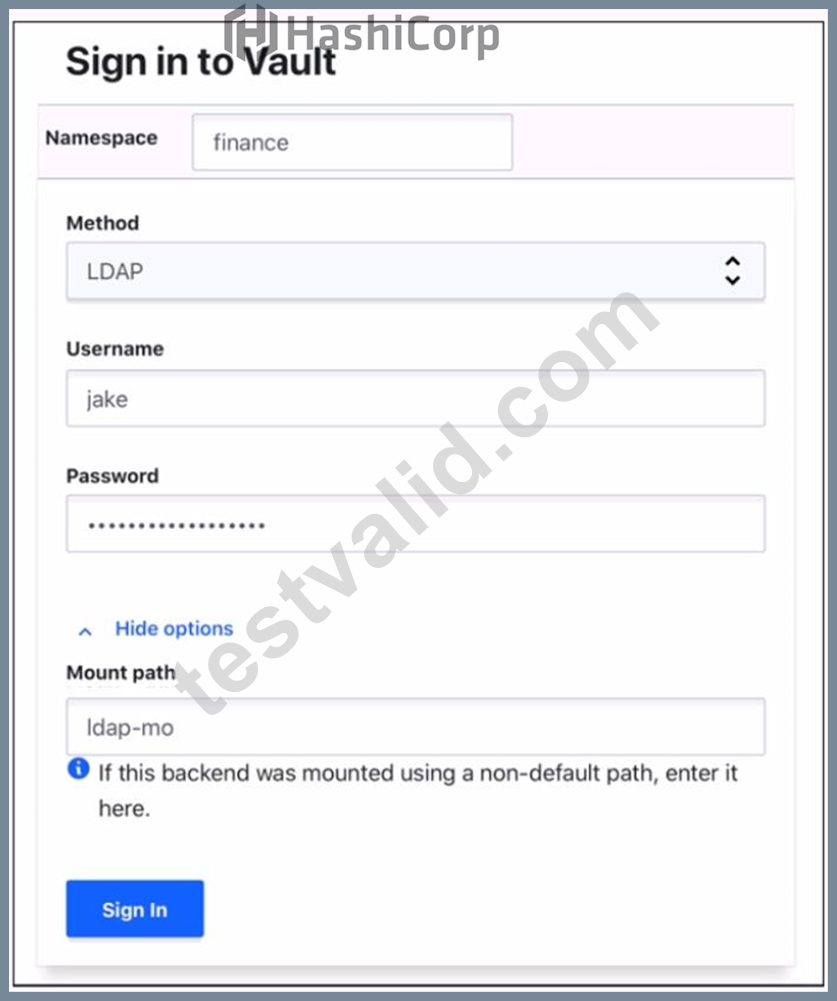
Answer:
Explanation: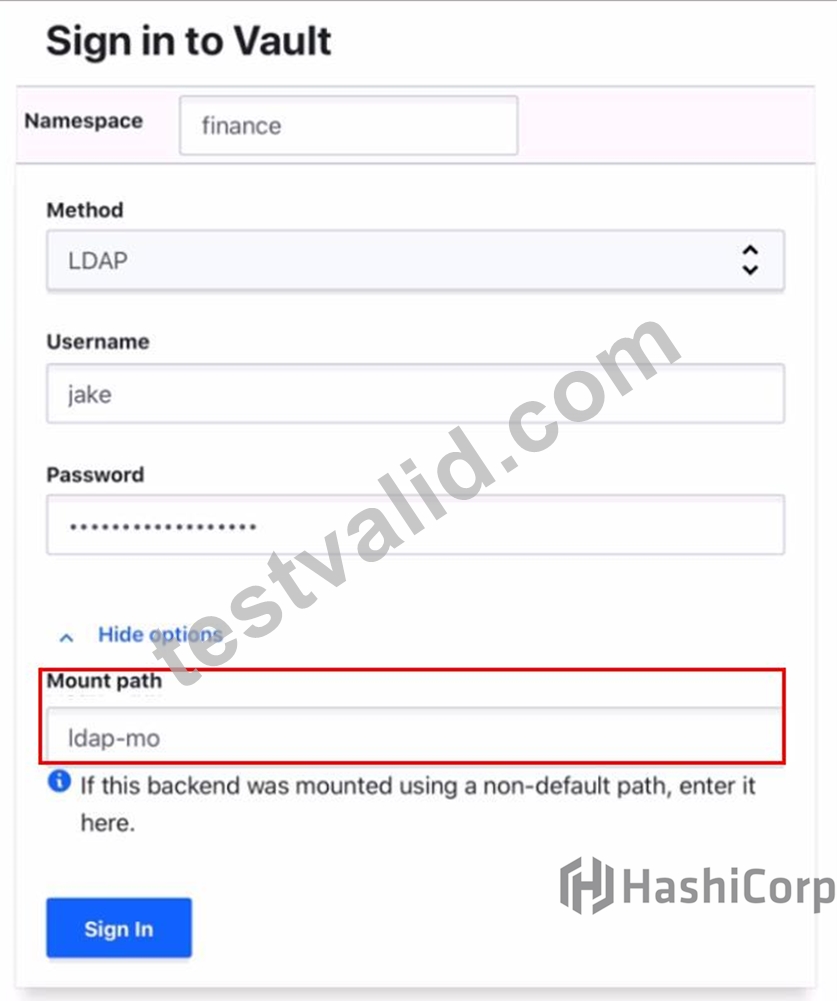
NEW QUESTION # 31
The key/value v2 secrets engine is enabled at secret/ See the following policy: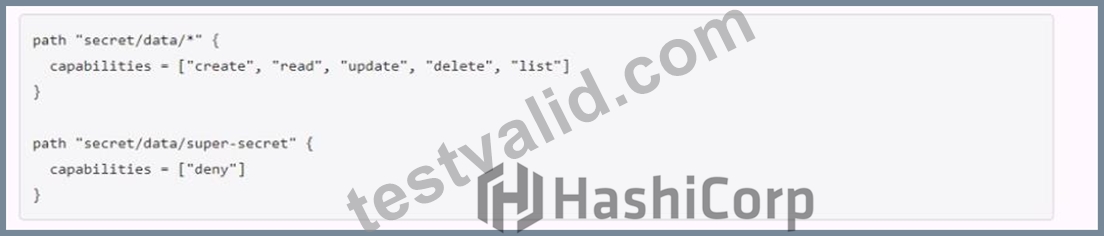
Which of the following operations are permitted by this policy? Choose two correct answers.
- A. vault kv delete secret/super-secret
- B. vault kv metadata get secret/webapp1
- C. vault kv get secret/webapp1
- D. vault kv list secret/super-secret
- E. vault kv put secret/webapp1 apikey-"ABCDEFGHI] K123M"
Answer: B,C
Explanation:
The policy shown in the image is:
path "secret/data/webapp1" { capabilities = ["create", "read", "update", "delete", "list"] } path "secret/data/super-secret" { capabilities = ["deny"] } This policy grants or denies access to the key/value v2 secrets engine mounted at secret/ according to the following rules:
The path "secret/data/webapp1" has the capabilities of "create", "read", "update", "delete", and "list". This means that the policy allows performing any of these operations on the secrets stored under this path. The data/ prefix is used to access the actual secret data in the key/value v2 secrets engine5. Therefore, the policy permits the operation of vault kv get secret/webapp1, which reads the secret data at secret/data/webapp16.
The path "secret/data/super-secret" has the capability of "deny". This means that the policy denies performing any operation on the secrets stored under this path. The policy overrides any other policy that might grant access to this path. Therefore, the policy does not permit the operations of vault kv delete secret/super-secret and vault kv list secret/super-secret, which delete and list the secret data at secret/data/super-secret respectively6.
The policy does not explicitly define any rules for the path "secret/metadata". The metadata/ prefix is used to access the metadata of the secrets in the key/value v2 secrets engine, such as the number of versions, the deletion status, the creation time, etc5. By default, if the policy grants any of the capabilities of "create", "read", "update", or "delete" on the data/ path, it also grants the same capabilities on the corresponding metadata/ path7. Therefore, the policy permits the operation of vault kv metadata get secret/webapp1, which reads the metadata of the secret at secret/metadata/webapp18.
NEW QUESTION # 32
Use this screenshot to answer the question below: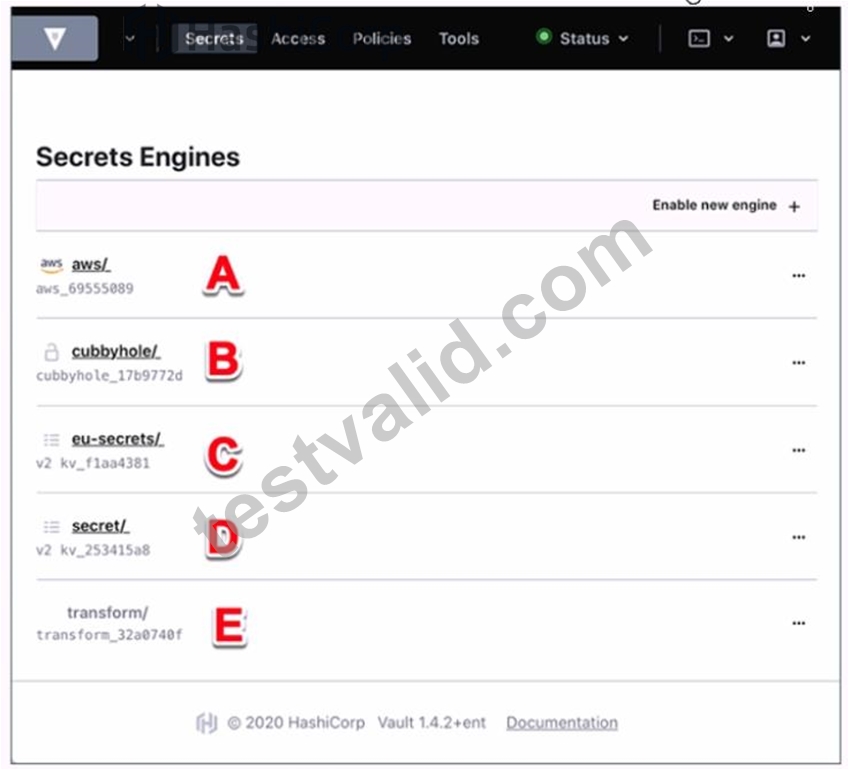
Where on this page would you click to view a secret located at secret/my-secret?
- A. E
- B. D
- C. B
- D. A
- E. C
Answer: E
Explanation:
In the HashiCorp Vault UI, secrets are organized in a tree-like structure. To view a secret located at secret/my-secret, you would click on the "secret/" folder in the tree, then click on the "my-secret" file. In this screenshot, the "secret/" folder is located at option C. This folder contains the secrets that are stored in the key/value secrets engine, which is the default secrets engine in Vault. The key/value secrets engine allows you to store arbitrary secrets as key/value pairs. The key is the path of the secret, and the value is the data of the secret. For example, the secret located at secret/my-secret has a key of "my-secret" and a value of whatever data you stored there.
Reference:
[KV - Secrets Engines | Vault | HashiCorp Developer]
NEW QUESTION # 33
Which of the following statements describe the CLI command below?
S vault login -method-1dap username-mitche11h
- A. By default the generated token is valid for 24 hours
- B. Generates a token which is response wrapped
- C. You will be prompted to enter the password
- D. Fails because the password is not provided
Answer: B
Explanation:
The CLI command vault login -method ldap username=mitchellh generates a token that is response wrapped. This means that the token contains a base64-encoded response wrapper, which is a JSON object that contains information about the token, such as its policies, metadata, and expiration time. The response wrapper is used to verify the authenticity and integrity of the token, and to prevent replay attacks. The response wrapper also allows Vault to automatically renew the token when it expires, or to revoke it if it is compromised. The -method ldap option specifies that the authentication method is LDAP, which requires a username and password to be provided. The username mitchellh is an example of an LDAP user name, and the password will be hidden when entered. Reference: Vault CLI Reference | Vault | HashiCorp Developer, Vault CLI Reference | Vault | HashiCorp Developer
NEW QUESTION # 34
As a best practice, the root token should be stored in which of the following ways?
- A. Should be stored in configuration automation tooling
- B. Should be stored in another password safe
- C. Should be revoked and never stored after initial setup
- D. Should be stored in Vault
Answer: C
Explanation:
The root token is the initial token created when initializing Vault. It has unlimited privileges and can perform any operation in Vault. As a best practice, the root token should be revoked and never stored after initial setup. This is because the root token is a single point of failure and a potential security risk if it is compromised or leaked. Instead of using the root token, Vault operators should create other tokens with appropriate policies and roles that allow them to perform their tasks. If a new root token is needed in an emergency, the vault operator generate-root command can be used to create one on-the-fly with the consent of a quorum of unseal key holders. Reference: Tokens | Vault | HashiCorp Developer, Generate root tokens using unseal keys | Vault | HashiCorp Developer
NEW QUESTION # 35
......
2024 Valid Vault-Associate test answers & HashiCorp Exam PDF: https://pass4sure.testvalid.com/Vault-Associate-valid-exam-test.html